Every action recorded. Nothing erased.
Log every AI request, policy decision, and administrative change with Immutable, tamper-proof audit trails that no user — including the Owner role — can delete or modify.
Tamper-proof Immutable Logs
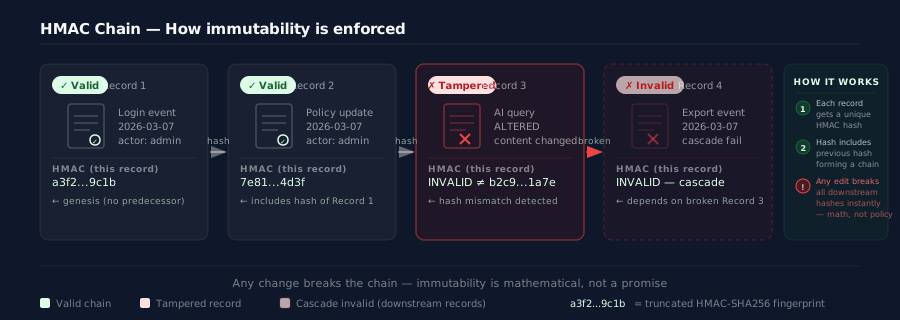
Every request, every policy evaluation, and every enforcement action is recorded in an append-only log. Each entry is cryptographically chained to the previous one cryptographically — tampering with any record breaks the chain and is detectable immediately. Logs cannot be deleted by any user, including accounts with the Owner role. IP addresses, routing decisions, and policy outcomes are all covered by the integrity chain. The audit trail is tamper-evident by construction, not by policy.
Geolocation and Network Enrichment
Every audit record captures source and destination IP addresses enriched with geographic and network metadata: country, region, city, ISP, and ASN. This enrichment is captured at the time the request is processed, not retroactively, ensuring accurate and contemporaneous context for every action. Use geographic patterns to detect anomalous access, verify traffic legitimacy, and demonstrate compliance with data residency requirements.
Signed Exports and Compliance Reports
Export audit logs with cryptographic signatures that external auditors can verify independently. Export gateway activity as SOC 2 audit evidence (audit preparation — not a completed SOC 2 report) — select a date range, choose the applicable controls, and Arbitex Gateway produces the evidence package. Exports include full request context: actor identity, timestamp, source IP, action taken, and before-and-after deltas for every administrative change.
Anomaly Detection and Alerting
Automated anomaly detection monitors access patterns, volume spikes, and policy override frequency across your audit trail. Alerts delivered via webhook to your configured endpoint. Configurable retention tiers — 30 days, 90 days, or 1 year and beyond — let you match log storage to your regulatory and operational requirements.
Signed Policy Bundle Verification
Policy bundles distributed to Hybrid Outpost nodes are cryptographically signed at the source and timestamp-verified on receipt. Nodes reject tampered or expired bundles by default — governance configuration cannot be silently replaced. Bundle signature status and last verified timestamp are surfaced in the admin dashboard for operational visibility.
How it works
Connect and configure
Point your AI traffic through Arbitex Gateway. Every request begins generating an immutable audit trail automatically. Configure retention tiers based on your compliance obligations.
Inspect the full record
Every log entry captures the complete context: actor identity, timestamp, source IP, policy evaluated, enforcement action, and content hash. Administrative actions are logged separately with before-and-after change deltas.
Export and report
Export gateway activity as SOC 2 audit evidence (audit preparation — not a completed SOC 2 report) from the admin console. Export signed audit logs for external review with cryptographic verification. Anomaly detection alerts notify your team when access patterns deviate from baseline.