AI in financial services needs more than a guardrail.
Route, inspect, and enforce policy on every AI request across trading analysis, risk modeling, and client communications. Card data blocked. Audit logs immutable. Data stays in your environment.
Capabilities
Card Data Detected Before It Reaches Any Model
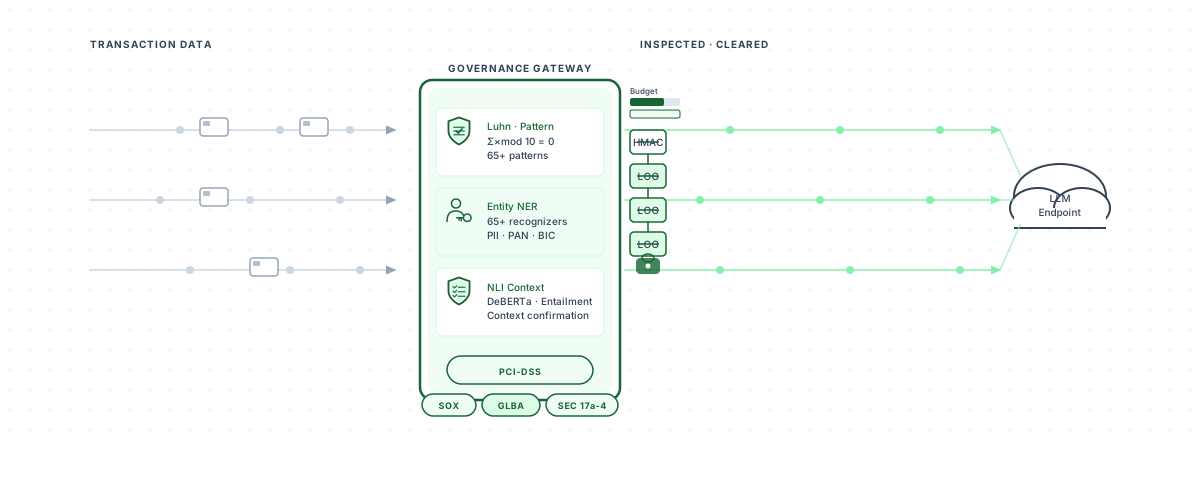
Every AI request and response passes through Arbitex's 3-tier DLP pipeline. Tier 1 applies 80+ detection patterns to identify Primary Account Numbers (PANs), CVVs, and expiration dates, with checksum validation where applicable (IBAN MOD-97, ABA routing, NPI Luhn, DEA check digit, ITIN, EIN, Canadian SIN, IMEI, SWIFT/BIC). Checksum validation confirms a matched number is structurally valid, not an arbitrary digit string, which keeps false positive rates low. PANs are blocked or redacted inline. Every detection is logged with pattern type, enforcement action, and timestamp. Designed to support PCI-DSS compliance requirements without adding a separate scanning layer.
Immutable Audit Logs Built for Regulatory Review
Every AI request and response is captured in an tamper-proof audit log. Records are immutable by construction — no user, including account owners, can modify or delete them. Signed exports support external verification. Configurable retention of one year or more supports SEC Reg FD record-keeping requirements for broker-dealers. Write-once, read-many architecture.
Policy Controls for Financial Data Environments
The policy engine enforces access controls by team and role. Financial data detection rules run in the DLP layer, and all policy changes are logged with before/after deltas — providing a tamper-evident record of configuration history. Designed for SOX and GLBA environments where access to consumer financial information must be restricted, logged, and auditable.
AI Spend Governed at the Team and Project Level
LLM costs are capped per team, project, and model. Token quotas and dollar budget limits enforce spend boundaries in real time. No request exceeds its assigned budget without an explicit policy change — which is itself logged.
How it works
Deploy the Outpost in your VPC
The Arbitex data plane installs in your cloud environment. AI traffic routes through it before reaching any model. The inspection engine, DLP pipeline, and audit logger run inside your infrastructure. Data never leaves your environment.
Configure compliance bundles and access policies
Apply pre-built compliance bundles for PCI-DSS, SOX, GLBA, and SEC environments. Set detection rules, enforcement actions (block, redact, flag), and access controls by team and role. All configuration changes are version-logged.
Every request inspected, logged, and enforced
From the first call, every AI request and response passes through the detection pipeline. Card data, consumer financial information, and transaction-related content are enforced per policy. The audit log captures the full record — available for internal review or regulatory submission.
Related Resources
Regulated AI adoption starts with the right infrastructure.
Arbitex gives financial services teams the governance layer to move fast without creating compliance exposure. Every call inspected. Every call logged.