AI governance for regulated financial institutions.
GLBA, SOX, BSA/AML, and SEC Reg FD compliance bundles active simultaneously. Card data blocked before it reaches any model. Audit logs immutable by construction. Data stays in your environment.
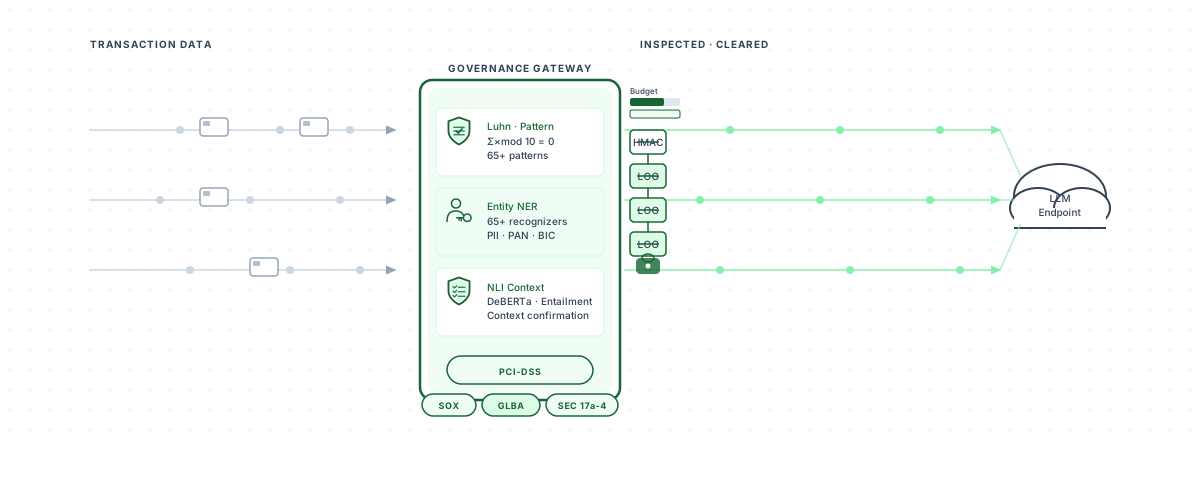
Compliance built for financial data environments.
DLP for PAN and Account Numbers
Arbitex applies Luhn-validated card number detection across every AI request and response — Primary Account Numbers, CVVs, and expiration dates are identified using pattern matching plus checksum validation. Account numbers, routing numbers, and SWIFT/BIC codes are caught by structured pattern matching. Matched financial data is blocked or redacted in-path before reaching any language model. Every enforcement action is logged with pattern type, action taken, and timestamp.
PCI-DSS Policy Packs
Pre-built compliance bundles map enforcement controls directly to PCI-DSS Data Security Standard requirements. Cardholder data detection rules, network segmentation validation, and access logging are configured as a single bundle. Every DLP detection rule aligns to a specific PCI-DSS requirement — Requirement 3 (stored data protection), Requirement 7 (access restriction), and Requirement 10 (monitoring and logging). No separate scanning layer required.
Credential Intelligence for Financial Systems
Financial institutions integrate AI tools with trading platforms, core banking systems, and payment gateways. Credential intelligence detects leaked API keys, database connection strings, service account credentials, and OAuth tokens in AI prompts before they reach model endpoints. Detected credentials are blocked or redacted in-path. Every detection is logged with credential type and source context for incident response and regulatory reporting.
Audit Trails for SOX Compliance
Sarbanes-Oxley Section 404 IT controls require that access to systems supporting financial reporting is restricted, logged, and auditable. Arbitex produces tamper-proof audit logs — every AI interaction, policy configuration change, and enforcement action is version-logged with before/after deltas. Write-once, read-many records satisfy SEC Rule 17a-4 requirements. Signed exports support SOX IT audit submissions and SEC examination requests.
Content Categories for Transaction Data
Content classification distinguishes transaction-related AI use cases from general business queries. Prompts containing MNPI, trade execution data, wire transfer references, and SAR documentation route through maximum-enforcement DLP policies. General business queries — internal comms, HR, marketing — apply lighter policies. Classification runs automatically using the content category engine, reducing false positives for non-regulated workflows.
Model Risk Management (MRM)
OCC SR 11-7 and FFIEC guidance require documentation, validation, and governance of models used in financial decision-making. Arbitex provides the logging and documentation infrastructure for AI model usage — every model invocation is recorded with provider, version, input classification, output classification, and enforcement action. Exportable audit records support MRM validation engagements for OCC-supervised and FFIEC-examined institutions.
How it works
Protect financial data
The Arbitex data plane installs in your cloud environment using Docker Compose or Kubernetes. AI traffic routes through it before reaching any model. The DLP pipeline detects card numbers, account numbers, NPI, MNPI, and transaction-related data using Luhn-validated pattern matching, format-specific recognition, and ML-based entity detection. Every financial identifier is caught before reaching a model endpoint.
Enforce regulatory policies
Apply pre-built compliance bundles for PCI-DSS, GLBA, SOX, BSA/AML, and SEC Reg FD. All bundles are active simultaneously under one policy configuration — no per-framework setup required. Content categories separate transaction data from general business queries for proportional enforcement. Detection rules, enforcement actions (block, redact, flag), and access controls are configured by team and role.
Prove compliance
From the first call, every AI request and response passes through the detection pipeline and generates an tamper-proof audit record. Write-once logs satisfy SEC Reg FD retention requirements. Signed exports support SOX IT audits, FinCEN inquiry responses, FFIEC examinations, and internal BSA/AML reviews. Every configuration change is version-logged with before/after deltas.
Six frameworks. One policy layer.
Each compliance obligation maps to a specific Arbitex capability. All bundles are active simultaneously — no separate configuration per framework.
Luhn-validated card number detection blocks PANs, CVVs, and expiration dates in-path. Detection logged with pattern type and enforcement action.
NPI detection across all AI interactions. Access controls enforced by team and role. Every NPI access logged with user context and policy version.
Access controls for AI supporting financial reporting. Configuration changes version-logged with before/after deltas for SOX IT audit submissions.
Complete chain-of-custody logging for transaction monitoring and SAR workflows. Supports FinCEN inquiry responses and internal BSA/AML audit submissions.
tamper-proof write-once audit logs. Configurable retention of one year or longer. Signed exports formatted for SEC and FINRA examination requests.
FFIEC IT examination guidance requires financial institutions to document, monitor, and control technology risks. Arbitex provides the governance layer for AI tool usage — every model invocation logged with provider, input classification, and enforcement action. Audit exports formatted for FFIEC examination submissions across all five federal banking regulators.
Related Resources
Regulated AI adoption starts with the right infrastructure.
Arbitex gives financial services teams the governance layer to move fast without creating compliance exposure. Every AI call inspected. Every AI call logged. Data never leaves your environment.